Mobile Operator Data Leak in Pakistan: PTA Rules Give the Operator 72 Hours to Report It and Bar Storing Your Data Abroad
PTA's telecom data security regulations give an operator 72 hours to report a breach and bar storing your data abroad without approval. See what you can do.
Short answer: PTA's Critical Telecom Data and Infrastructure Security Regulations say a mobile operator must tell PTA within 72 hours of discovering a data breach. They also say your data may only be used for the purpose it was collected for, and may not be stored outside Pakistan without PTA's approval.
Your SIM company holds more about you than most people notice. It has your name, your CNIC number, your call records, your IP address and the numbers you call. When that data leaks, the first question is who must tell whom, and how fast.
We read the regulations on PTA's regulations page on 13 October 2026. The PDF there is the 2020 notification, S.R.O. 1226(I)/2020, in the Gazette of 18 November 2020. It applies to every PTA licensee, so it covers mobile operators and internet providers. We read it as a text file, and quote only what it says.
What PTA counts as your critical telecom data
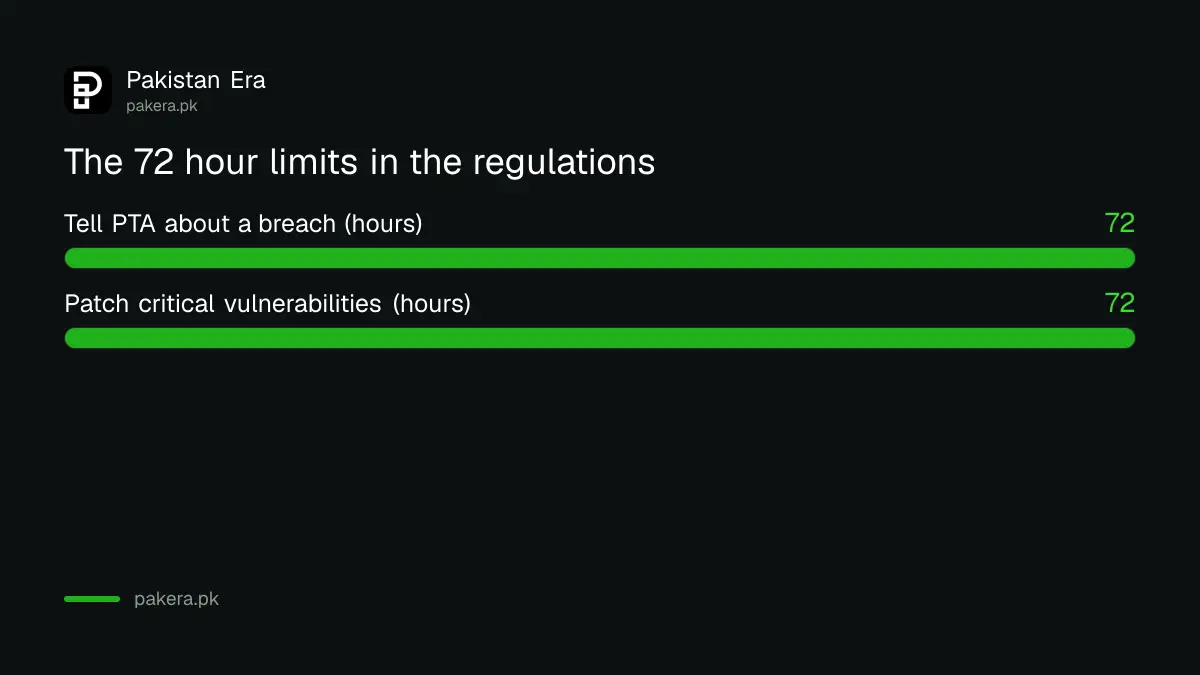
The regulations define personal data as information linked to a person or organisation. The list in the text includes name, parents' names, address, photo, CNIC or passport number, call data records, IP address details, social media accounts, phone numbers and websites.
A call data record, or CDR, is the log of who called whom, when and for how long. The regulations treat it as personal data. Critical telecom data also covers anything vital to the secrecy and security of the operator's systems, including voice and data communication.
Your operator may use this data only for the purpose it obtained it for. That is a plain duty in regulation 8. The data must be protected against disclosure, change, loss and destruction.
An operator has 72 hours to tell PTA about a breach
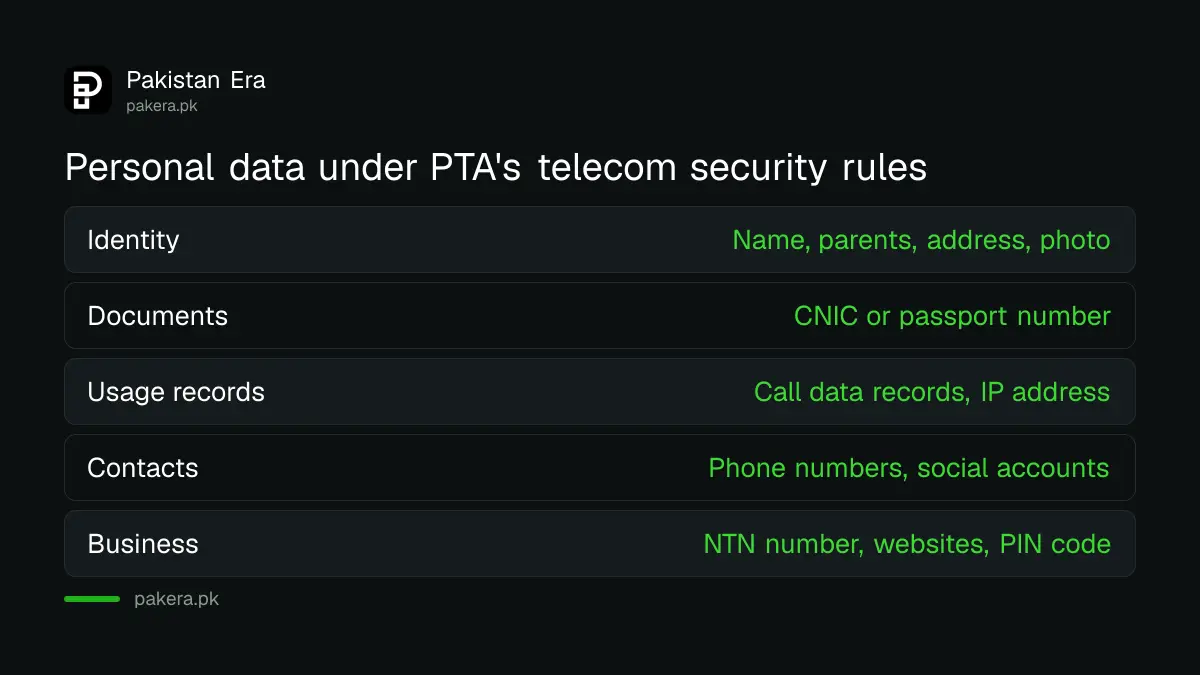
Regulation 18 says that in case of a data breach, or damage to critical infrastructure or data, the licensee shall inform PTA within 72 hours from the discovery of the incident. The clock starts at discovery, not at the date the breach began.
The same regulations say critical software patches must be applied and verified within 72 hours. A data breach is defined as intentional or unintentional release of stored information to an entity not authorised to access it. A mistake counts, not only a hack.
The rule is a duty to inform PTA. We did not find a line that says the operator must also tell you, the subscriber. If you are told, it will be because the operator chose to, or because another law or a PTA direction required it.
| Duty of the operator | Time or limit | Regulation |
|---|---|---|
| Inform PTA of a data breach | 72 hours from discovery | 18 |
| Patch critical vulnerabilities | 72 hours, applied and verified | 10 |
| Store data outside Pakistan | Not without PTA approval | 8 |
| Use data | Only for the purpose it was obtained | 8 |
| Security testing | Vulnerability testing at least every 6 months | 13 |
| Independent review | At least once a year, with PTA approval | 13 |
Your data cannot be stored abroad without PTA's approval
Regulation 8 says no data shall be stored beyond the country's geographical boundaries without PTA's approval. This matters for cloud services and for operators with foreign parent companies.
The text does not publish a list of approvals, and we did not find one on PTA's page. We also cannot say which operators have approval for which data.
Operators must also keep the licence's data retention periods, and ask PTA where a period is not stated. How long your records are kept is a separate question, covered for public Wi-Fi in PTA's data retention rules for hotspots.
Operators must give you a way to report a security event
Regulation 11 says each operator must run a computer emergency response team with designated channels so that users, subscribers and other sources can report cybersecurity events. It also says operators must give customers awareness of security threats.
That gives you a duty to hold them to. If you suspect a leak, such as callers who know your CNIC or your account details, you can report it through the operator's channel and ask for a reference number.
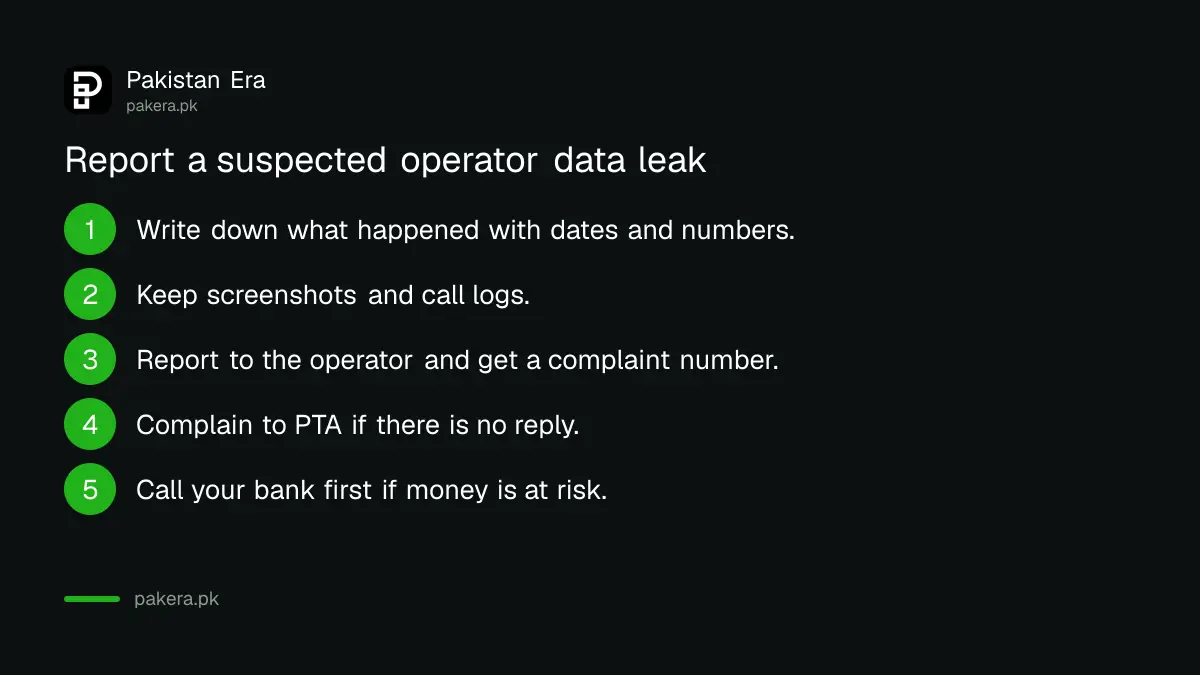
- Write down what happened, with dates and the numbers that contacted you.
- Keep screenshots of messages and call logs.
- Report it to the operator's security or complaint channel and ask for a complaint number.
- If there is no reply, file a complaint using the PTA complaint steps.
- If money is at risk, call your bank first, then follow how to report a fake call or SMS scam.
What the rules do not promise you
The regulations set duties on operators and powers for PTA. They do not set a compensation amount for a subscriber, and we found no refund rule. PTA may act against an operator that does not comply, on information from any source.
The regulations are also from 2020. PTA's later consumer rules add a confidentiality duty on operators in the Telecom Consumers Protection regulations, as covered in the operator helpline and billing standards. For leaks of your passwords from other sites, use a breach check for your passwords.
Common questions
How fast must an operator report a data breach to PTA?
Within 72 hours from the discovery of the incident. The rule covers data breaches and damage to critical telecom infrastructure or critical data.
Must the operator tell me if my data leaks?
We found no such duty in these regulations. They require the operator to inform PTA. Ask your operator in writing if you suspect a leak.
Can my data be stored on servers abroad?
Not without PTA's approval, under regulation 8. We could not find a public list of approvals, so we cannot say who has one.
What counts as personal data in these rules?
Name, parents' names, address, photo, CNIC or passport number, call data records, IP address details, social media accounts, phone numbers and websites.
Where do I report a suspected leak?
Start with the operator's reporting channel, then PTA's complaint system with your proof. Report fraud attempts to your bank immediately.
How we verified this
What we checked, where we read it, and what we could not confirm.
Last checked on 13 October 2026, Pakistan time. We read the Critical Telecom Data and Infrastructure Security Regulations on PTA's regulations page. The PDF there is the 2020 notification. We could not confirm whether PTA has replaced it with a newer version, whether any operator has been penalised under it, or how many breaches have been reported.
About the author
Technology Journalist & Multimedia Producer
Ahmad Ali is a technology journalist and multimedia producer at Pakistan Era, joining the team in October 2026. He covers consumer technology and digital life for Pakistani readers, combining research with hands-on product testing.